Establish timing and responsibility
Identify who performs technical actions and who decides how business content will be handled. Record the agreed time for changes. Follow the organisation's process instead of treating an informal message as a reason to delete accounts broadly on your own initiative.
List the affected systems: device sign-in, email, shared storage, specialist applications and separately managed services. A central identity system may cover many of them but not every external account. Inspect the actual equipment and access record, not only one administration portal's user list.
Transfer work rather than sharing an identity
Assign ongoing projects, shared files and open enquiries to a new responsible person. Use the intended sharing or transfer functions. Passing on the departing person's password confuses identity and responsibility and is not a clean technical handover.
For services with an individual owner, check how the documented ownership-transfer process works. A team may be able to read a file without being able to manage its sharing settings or automation. Test access with the actual successor's account before removing the previous route.
Distinguish blocking, sessions and retention
Blocking sign-in, ending existing sessions, removing a licence and deleting an account are separate operations. Their effects and timing depend on the service. Follow the official instructions for the service in use and record which action has actually completed.
Before deletion, establish what must remain under organisational requirements. This article does not set a retention period. Where personal or business records create uncertainty, the responsible team determines the scope and permitted access. Technical work should implement that decision rather than silently substitute for it.
Receive equipment and accessories
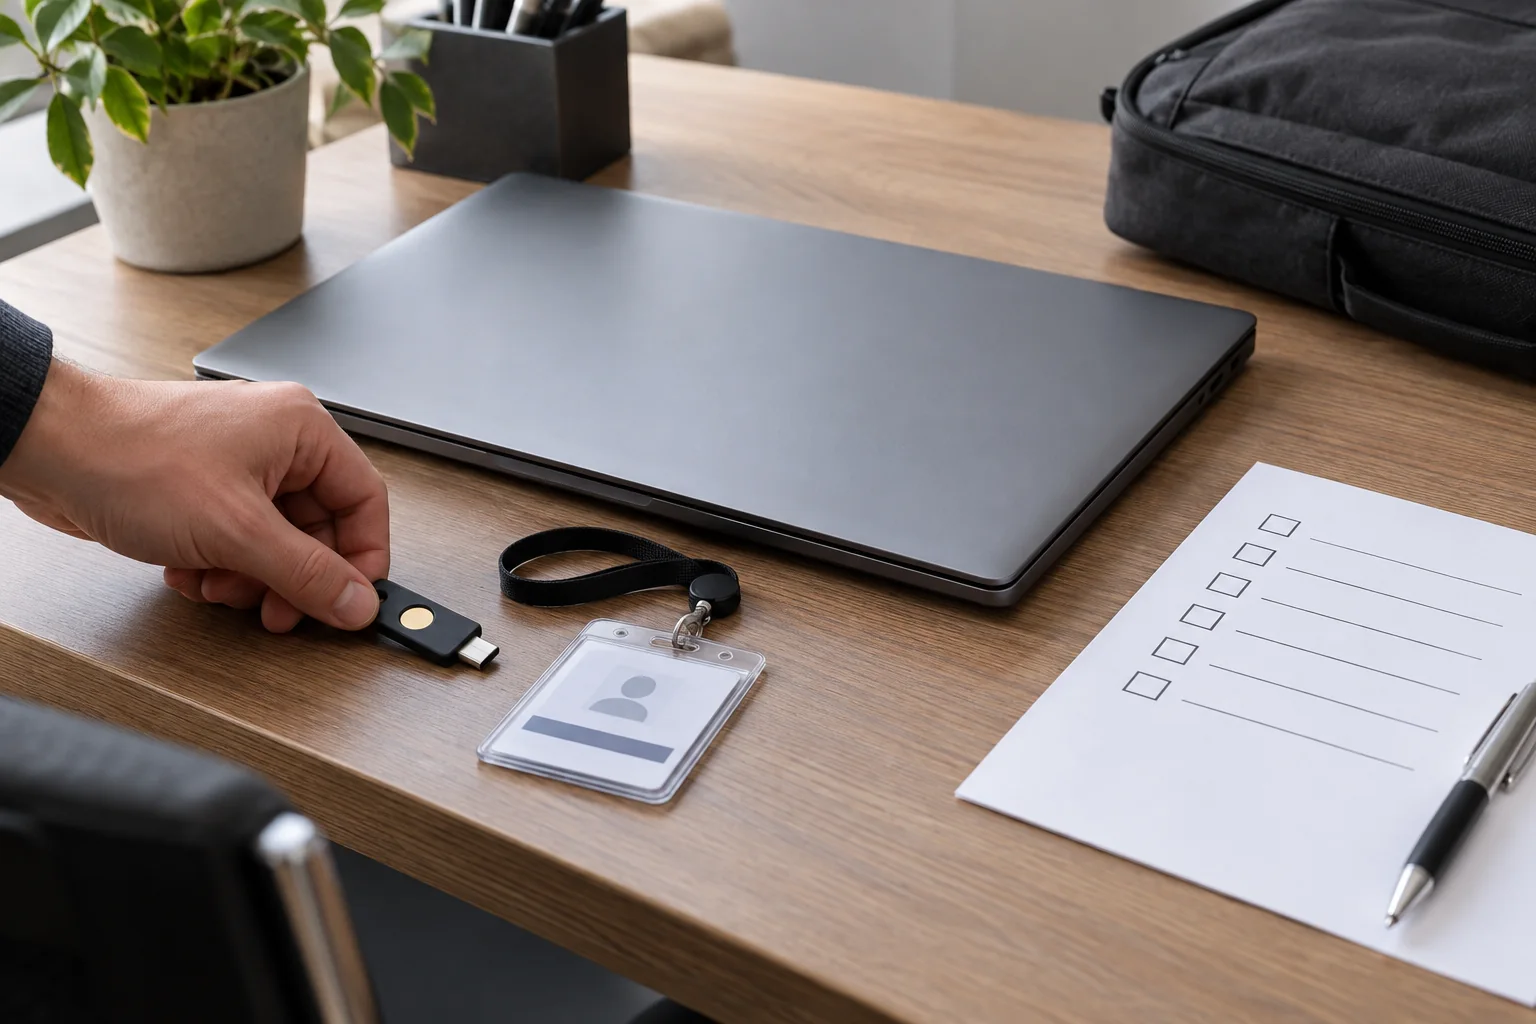
Compare returned items with the inventory and record missing accessories or visible damage. Track power adapters, security keys and issued storage devices clearly. A laptop alone is not necessarily the complete equipment originally provided.
Reset equipment only after required data transfer and authorisation have been addressed. Remove it from management systems using the intended procedure. Its next user should receive their own configured access instead of inheriting the previous user's unchanged session.
Verify the conclusion
With a responsible person, confirm that new owners can perform their tasks and that the intended old access has ended. Record exceptions with a reason, owner and review date. Marking a task complete without understanding the remaining services provides little assurance about the actual outcome.
Keep a concise technical completion record in an appropriate restricted location. It should describe actions and responsibility, not contain secret credentials. This leaves a later reviewer able to understand why equipment was ready for reuse and who took ownership of a particular area of work.